
TL;DR: HR system cyberattack lessons for small employers
An HR system cyberattack hit the European Commission's payslip and leave platform Sysper and its medical claims system, POLITICO reported on 19 November 2026, after over 10 days of disruption. Salaries landed, but staff couldn't log leave and say they were told little. Whether staff data was compromised is unknown. Your fallback: an offline payroll copy, a manual pay run, a staff message and the GDPR 72-hour rule.
Developing story. Last updated 19 Nov 2026, 11:35 CET. We'll update this article as the Commission and CERT-EU publish more.
Here is what happened in the European Commission cyberattack, on our sister site MeanCEO. This one is for women founders and small business owners who employ people.
What do we know so far about the HR system cyberattack?
POLITICO's Brussels Playbook broke the story on 19 November, citing EU officials and a leaked internal email. It reports:
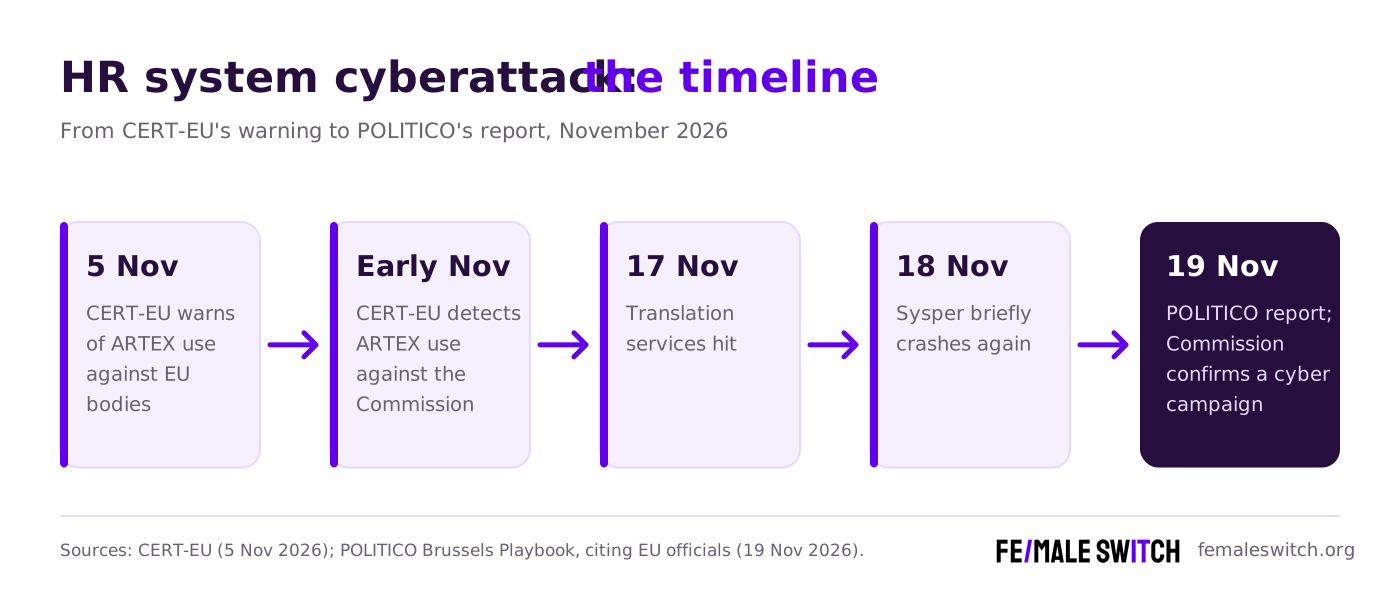
- Sysper, the HR platform for payslips, leave and timesheets, and MyPMO, the medical reimbursement system, were hit. Both "were restored earlier this week", then Sysper "briefly crashed again" on 18 November.
- Pay arrived: salaries "landed as usual", but some officials couldn't log timesheets or leave.
- Staff heard little. Three officials complained, and an IT reply blamed "a general issue affecting the system's functionality" without mentioning a cyberattack.
- The tool: CERT-EU, the EU bodies' cyber team, detected hackers using ARTEX, a public AI tool that finds weak spots in software. It had warned on 5 November of likely ARTEX use against EU bodies.
Spokesperson Thomas Regnier confirmed a "detected cyber campaign": "Individual systems were targeted and, in line with our standard practice, we have informed those concerned." He named no data or attacker.
What we don't know yet
- Whether staff data was accessed or copied. Investigators are "still trying to establish" that, POLITICO writes, which an official said explains the limited communication.
- How the attackers got in, and who they are. Nobody has claimed the attack, and nothing reported points to users outside the Commission.
Timeline
Could an HR system cyberattack hit a small employer?
Your payroll tool holds the same kind of data as Sysper and MyPMO: bank details, salaries, sick notes and leave records. The FBI's ARTEX warning says such tools go after "peripheral systems" like employee apps, some reaching privileged access "in under three hours". Read how ARTEX works and our checklist for the doors ARTEX finds at small businesses.
What should you do if your payroll or HR software goes down?
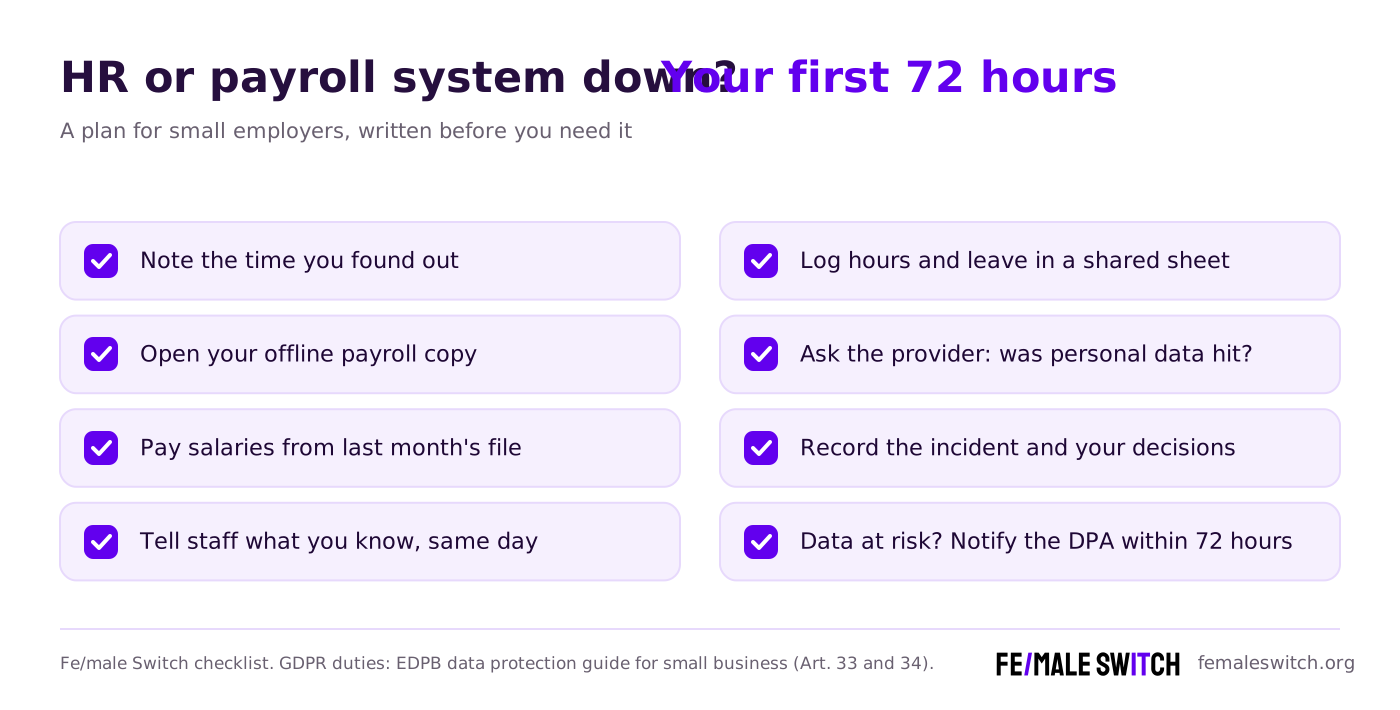
- Keep an offline payroll copy. After every pay run, export net pay, bank details and leave balances to an encrypted file you control.
- Prepare a manual pay run. Save last month's bank batch payment file, so you can pay from your bank's app and fix payslips later.
- Tell staff the same day: what is down, that pay day stands, how to log hours and leave meanwhile, and when you'll update them. Commission staff complained about silence.
- Record everything: when you found out, what you checked and who decided what.
- Ask whether personal data was touched. If yes, the GDPR 72-hour clock below has started.
When does the GDPR 72-hour rule apply?
Only when personal data is involved. The EDPB's guide for small business counts incidents affecting its "confidentiality, integrity or availability", so staff records locked by ransomware count. The clock starts at "a reasonable degree of certainty" that personal data was compromised, and you can notify "in several steps".
Ireland's Data Protection Commission sets the same 72 hours; see our GDPR guide for startups.
What should you ask your HR or payroll provider?
- How fast will you tell us about a breach? A processor must notify you "without undue delay"; put it in the contract.
- Can we export all payroll and leave data ourselves, in a file we can open without your software?
- How long does a full restore take, and when did you last test it?
- Is two-step login (MFA) on everywhere?
If the provider is hit, follow our first 72 hours after a supplier data breach guide. Hiring your first employee? Set this up before day one.
Building a company that pays people on time?
The Fe/male Switch startup game takes you from idea to first paying customers in weekly quests, with an AI co-founder and a community of founders.
👉 Start the game
FAQ: HR system cyberattack
What is an HR system cyberattack?
An attack on software holding staff records like payslips and leave. At the Commission, POLITICO reports it hit Sysper and MyPMO.
Was Commission staff data stolen?
Unknown so far. Investigators are still checking, POLITICO reports; the Commission has named no data and no attacker.
Do I have to report it if my payroll provider is hacked?
Your provider must tell you without undue delay. If staff data is at risk, you notify your data protection authority within 72 hours, unless the breach is unlikely to put people at risk.
How do I pay staff if payroll software is down?
Pay from last month's bank batch file and offline pay data, then fix payslips once the system is back.
